THE LINUX FOUNDATION PROJECTS
Yearly Archives

2026

Welcome to the June 2026 Newsletter

By Newsletter

TL;DR | What’s in This Issue?

  • The redesigned CCC website launched June 23rd! 🎉
  • Confidential Computing Summit 2026 wrapped in San Francisco; session recordings are now live on the Linux Foundation YouTube channel.
  • TAC approved Blueprint C (Collaborative Clean Room), moved Keystone to emeritus, and the SPDM project hit a major post-quantum cryptography + FIPS 140-3 milestone.
  • NVIDIA Confidential Computing is now powering Apple’s Private Cloud Compute on Google Cloud.
  • The Academic Research Grant program received 35 proposals; two recipients to be announced July 1.
  • The GRC SIG is calling for contributors, especially from regulated industries working on confidential AI governance.

From the Executive Director 

Hello Community Member,

This month has been a busy one, with huge updates from the Outreach team (see below), a new strategic kick-off with the Governing Board (details to follow), continued strong engagement with Regulators and Standards Bodies and conferences in Mumbai (Open Source India) and San Francisco (Confidential Computing Summit).

And it feels like things have changed since this time last year: Confidential Computing has gone past an inflection point, with significant increases in adoption (Anthropic and Apple both gave keynotes where they made it clear that Confidential Computing is no longer optional: it’s foundational) and two (often overlapping) use cases where there is no question that CC is required: AI (both “standard” and Agentic) and Digital Sovereignty. The fact that there is overlap between these two should surprise nobody: everyone is using AI, and everyone cares (or should care) about their data, models, and applications. It has become clear to industry, and is becoming clear to governments and regulators, that the only way to secure your data against the myriad attackers is to use Confidential Computing. Confidential Computing, then, is a technology whose time has come: at the CCC, we plan to encourage and simplify adoption, push forward on new technologies and ensure that open source is placed squarely in the centre of the ecosystem. Join us!

From the Outreach Committee Chair

The redesigned CCC website launched on June 23rd, just in time to provide those attending CC Summit with an updated opportunity to learn more about how Confidential Computing works and how the CCC continues to shape the technology journey. The goal of the web redesign was to provide a customer experience that matches how the modern search is occurring – guided heavily by SEO and AI model use best practices. Executives can quickly and easily see how CCC helps reduce hidden regulatory and liability exposure, turn compliance into competitive advantage, enable high‑value data sharing without surrendering control, and support cloud and AI adoption on a hardware root‑of‑trust. The developer journey allows them to delve into the technical advancements made possible through the CCC.

We also added all new use cases make the impact of CCC collaboration tangible: secure fraud detection and AI model training on customer data without exposure in finance, privacy‑preserving clinical collaboration and AI diagnostics in healthcare, post‑cookie audience matching and tamper‑resistant clean rooms in AdTech, and sovereign, attested AI workloads and multi‑agency data sharing with cryptographic audit trails in government.

In addition to these new use cases, the Board Ready Guide to Confidential Computing provides a board-ready framework for understanding the regulatory, financial, and business opportunities of securing data-in-use with Confidential Computing. A special thanks to all of the outreach partners at AMD, Google, Linux Foundation, Intel, and NVIDIA who prioritized getting the site updated before CC Summit.

Speaking of the CC Summit 2026… the two days spent in San Francisco highlighted that Agentic AI has completely shifted the conversation from: how can the CCC drive awareness and adoption around this important technology to: how fast can we get it into the hands of customers today?

Many of the CCC members shared their expertise from the impact of agentic AI and securing workloads during inference, advancing business insights across every vertical, attestation and how best to fine tune CC to ensure optimal performance. The CCC shared the importance of standards, blueprints, and open source infrastructure.

If you weren’t able to be there in person, no need to fret, as sessions will be available on the Linux Foundation landing page soon, which can be found here.

Engage with the CCC and our latest posts on LinkedIn. Feel free to tag your company if you are highlighted and do share what you loved most about the event with us, so we can spotlight your feedback in next month’s update!

Outreach Resources

From the TAC

TAC had a busy lead-up to the Confidential Computing Summit, with two meetings in late May and early June covering project milestones, annual reviews, governance discussions, and a standout Tech Talk.

Blueprint C approved. The TAC formally approved the Collaborative Clean Room blueprint, authored by Mingshen Sun (TikTok) and Rene Kolga (Google). The document will now go through LF Creative for PDF layout and publication on the CCC website. This is the third in a series of blueprints the TAC has been developing to provide practical adoption-focused guidance for Confidential Computing deployments.

Keystone moves to emeritus. The Keystone project was voted to emeritus status, marking the end of its active lifecycle within the CCC. Keystone made important contributions to the evolution of Confidential Computing, and the TAC acknowledged the work of its maintainers. Should community interest arise in the future, the project can be revived from its archived state.

SPDM project hits PQC milestone. Duan presented the SPDM-RS annual review, highlighting a significant achievement: full SPDM 1.4 support including post-quantum cryptography algorithms ML-DSA and ML-KEM, cross-tested for interoperability with DMTF’s libspdm implementation. The project also gained a new adoption use case, live migration of Trust Domains, where SPDM establishes the secure session for exchanging migration keys between hosts. The team is evaluating new formal verification tools (Kani and Verus) to replace older tooling that has fallen out of maintenance, and the project maintains a strong 97% OpenSSF Best Practices badge score. SPDM key exchange has also been officially recognized in the FIPS 140-3 implementation guidance, a notable milestone for the protocol.

Open Enclave SDK annual review. Radica presented the Open Enclave SDK’s annual review, now in its fourth year as a CCC project. The project continues to be maintained on a six-month release cadence (currently v0.19.15), with around 65 weekly commits, 225 cumulative contributors, and 1.2k GitHub stars. Recent work includes support for TDX live migration attestation verification claims and updates to align with the latest Intel PSW releases. The team is working on removing legacy OP-TEE code and has improved its OpenSSF Best Practices badge from 75% to 84%. The project is not seeking graduation at this time but remains a stable part of the CCC portfolio.

Tech Talk: Portable Machine Image (PMI). Nathaniel McCallum (AMD) delivered a deep technical presentation on the Portable Machine Image format, a new approach to moving guest firmware entirely into the tenant’s software supply chain. The core problem PMI addresses is that in today’s CVM deployments, the firmware running inside the guest is selected and controlled by the cloud provider, not the tenant. As the French regulator ANSSI noted in their 2025 position paper, this makes it impossible for users to fully verify their trusted computing base. PMI solves this by defining an explicit, versioned launch contract, bundled as a PE artifact containing platform definitions, boot payloads, and per-target launch recipes, that any compliant hypervisor can execute deterministically. The same PMI image produces the same attestation measurement regardless of which cloud or hypervisor runs it. McCallum demonstrated the tooling live, showing a full guest boot in roughly 300 milliseconds using a minimal safe-Rust bootloader called Tattoo (approximately 12,000 lines of code, compared to OVMF’s 3.6 million). The talk sparked active discussion about operationalizing this in hyperscaler environments and its implications for portable attestation. You can watch the full talk on our Tech Talk Playlist.

GRC SIG: call for participation. Mark Novak (JPMC) presented on the state of the Governance, Risk, and Compliance SIG, which has published three governance patterns to date (workload governance, workload upgrade governance, and verifier governance) with a fourth on proxying gateways now in PR for TAC review. Mark emphasized that governance guidance is essential for unlocking adoption in regulated industries, and shared that the patterns are already being used to develop internal control objectives at JPMC. However, the SIG has been struggling with low participation and needs contributors to continue its work, particularly on upcoming patterns for confidential AI training and inferencing. The TAC is exploring options including integrating GRC working sessions into regular TAC meetings. If your organization deploys or plans to deploy Confidential Computing in a regulated environment, this is a great opportunity to contribute.

CC Academic Research Program. The program committee received 35 research proposals from researchers globally and is currently working through selections, with plans to sponsor two projects.

Looking ahead. The June 25 TAC meeting was cancelled due to the Confidential Computing Summit (June 23–24). TAC members planned an informal in-person meetup during the summit. The next regular meeting is July 9, with Rene Kolga chairing.

Join us at our meetings on alternating Thursdays at 7 am Pacific time. You can look up the meeting in your own timezone using the CCC Calendar. Recordings of past meetings are available on the YouTube TAC Playlist.

Recent News

New CCC Blog: Agentic AI Security is Moving Fast. Here’s Where to Start.
Outreach Chair Laura Martinez published a practical guide for enterprises navigating agentic AI security, making the case that traditional security frameworks weren’t built for autonomous AI workloads and explaining why hardware-based TEEs – now extending from CPU to GPU – are the necessary foundation.

👉 Read the blog
Let’s grow our community! Share this with your network.
Subscribe to the Newsletter!

Agentic AI Security is moving fast. Here’s where to start.

By Blog

By Laura Martinez, Chair of Outreach Committee, Confidential Computing Consortium

Agentic AI is moving faster than most security frameworks were designed to handle, and the organizations deploying it, including some of the most sophisticated enterprises in the world, are navigating new territory. The question isn’t whether your team is experienced enough. It’s whether the security model you’re working with was built for this moment.

The gap traditional security doesn’t reach

The Confidential Computing community has long understood something the broader security world is catching up to: encrypting data at rest and in transit leaves a critical window open. When data is actively being processed, it has to be decrypted. In a standard cloud environment, that moment of computation is exactly when it’s most exposed.

For years, that gap was an acceptable tradeoff. Workloads were bounded. Humans were in the loop. The blast radius of a compromised execution environment was contained.

Agentic AI changes all of that at once.

An AI agent executing autonomously across enterprise infrastructure isn’t a bounded workload. It’s continuously processing sensitive data, calling tools, accessing live data pipelines, and making decisions, all without a human checkpoint, and all inside a cloud environment where the hypervisor, the host operating system, and the cloud operator sit above the workload in the trust hierarchy. The assumption that the infrastructure that traditional security was built on is trustworthy  no longer holds when the workload is this autonomous.

Hardware-based Trusted Execution Environments address this directly. By creating isolated execution environments where memory is encrypted and managed at the CPU level, they make the underlying infrastructure irrelevant to the trust model. The hypervisor, the host OS, and the cloud operator are no longer in the trust boundary. The silicon is.

Why the GPU layer matters for agentic AI

Most enterprise security conversations about AI are still CPU-centric. But agentic AI workloads are GPU-heavy by nature. Inference, reasoning, and multi-step planning all run on GPU infrastructure. And extending the Confidential Computing trust boundary from the CPU to the GPU has been one of the industry’s most important recent advances.

GPU-side Confidential Computing means the trust chain can now extend from the CPU through a trusted and attested interconnect to the full inference stack. The agent’s reasoning, the model weights it runs on, and the data it processes can all sit within a hardware-rooted boundary. For organizations running agentic AI at scale, that progression closes the last major gap in the end-to-end trust architecture.

The deployment layer: making this real without rebuilding everything

Hardware-rooted trust at the CPU and GPU layer is the foundation. But for most enterprise teams, the practical question is how to deploy it without rebuilding their entire infrastructure stack.

Confidential containers on Kubernetes are one answer to that question for cloud-native environments. By running pods inside hardware-isolated virtual machines, memory inside the container becomes invisible to the host OS and the underlying administrator. Secrets are provisioned only after the execution environment has been verified through attestation. For organizations already running AI workloads in cloud-native environments, this is a clear path from awareness to production without a full infrastructure rebuild.

Attestation: the trust anchor for autonomous systems

Across all of these layers, the mechanism that ties everything together is cryptographic attestation. Before any sensitive data enters a Trusted Execution Environment, the TEE generates verifiable cryptographic proof of its hardware and software state. That proof can be verified remotely, confirming that the agent is running unmodified code in a genuine, trusted environment and can even be repeated at various points in the lifecycle to ensure continued security. Attestation is what makes Confidential Computing different from every other privacy-enhancing technology. It doesn’t just claim security, it proves it.

For an autonomous system operating with no human oversight, attestation is the architectural trust anchor. It answers the question every enterprise security team needs to be able to answer: how do we know the environment our AI is running in hasn’t been compromised?

Open standards: the CCC’s role in making this interoperable

The hardware is here. The deployment tooling is maturing. What the industry now needs is open, vendor-neutral guidance that helps organizations navigate the best technology stack choices, validate their architectures, and move confidently from evaluation to production.

Adoption-focused technical guidance and reference architectures, built collaboratively across hardware vendors, cloud providers, and software developers, designed to give enterprise teams a practical and interoperable path forward regardless of which cloud or hardware stack they’re running on.

The goal is straightforward: make Confidential Computing the default for AI infrastructure, not a specialized capability reserved for the most security-conscious organizations.

The conversation we want to have with you

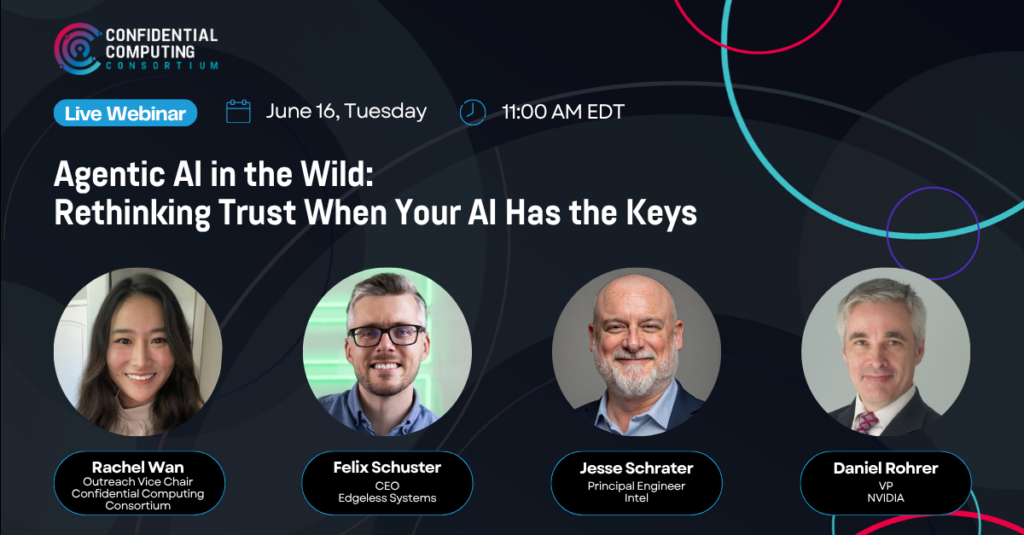
We’re bringing together three of the people closest to this problem for an open, practical conversation about what securing agentic AI actually looks like at every layer of the stack.

Felix Schuster, CEO of Edgeless Systems, is a pioneer in the Confidential Computing (CC) space, creating usable and deployable across every vertical. Jesse Schrater is a hardware visionary in the CC space, and brings Intel’s perspective on hardware-rooted trust and enterprise adoption of TDX and SGX. Daniel Rohrer from NVIDIA has been at the forefront of extending Confidential Computing at rack scale across CPUs, GPUs and networking where agentic AI and the world’s largest models and workloads run.

Together we’ll walk through LIVE the architecture, the deployment reality, and the practical steps organizations can take to start building AI infrastructure that’s secure by design.

Agentic AI in the Wild: Rethinking Trust When Your AI Has the Keys

Confidential Computing Consortium hosted live webinar ahead of CC Summit 2026.

This is the conversation the Confidential Computing community needs to be leading. We’d love for you to be part of it.

[Register here]

Welcome to the May 2026 Newsletter

By Newsletter

TL;DR | What’s in This Issue?

  • The Confidential Computing Summit 2026 is locked in for June 23–24 in San Francisco, focusing on securing enterprise Agentic AI.
  • The TAC approved and published the “3 Degrees of Confidential Computing” white paper, establishing a 3-level stack-integration maturity model.
  • The Coconut SVSM project expanded its mission from securing confidential VMs to supporting broader, general confidential workloads.
  • Sweden’s Data Protection Authority (IMY) issued landmark, first-of-its-kind GDPR guidance on using TEEs for off-premises data processing.
  • A redesign of the CCC website landing page is currently underway and open for member feedback to improve user experience.
  • The 2026 Academic Research Grant program is wrapping up its open call, with applications officially closing on June 1st.
  • Digital marketing momentum spiked sharply in April, yielding a 64% increase in social media impressions and a 56% bump in engagement.

From the Executive Director 

Hello Community Member,

One of key conferences in the Confidential Computing Calendar, Confidential Computing Summit, is just around the corner, starting on the 23rd June and I’m looking forward to meeting folks there, so if you’re attending, please let me know so we can get together. If you can’t wait that long for Confidential Computing content, or you’re based in Asia, then I’ll also be attending and speaking at Open Source India the week before. I’m not the only person speaking on Confidential Computing, and it’s great to see several topics making it onto a really packed schedule for the conference. Again, if you or anyone in your ecosystem will be attending, I’d love to meet up.

Last month also saw Consensus Miami, a blockchain, Web3 and decentralized computing conference. I was cheered to see the number of companies considering or actively employing Confidential Computing in this space, which looks set to become a real growth sector for CC. A workshop on Verification of AI Development in San Francisco highlighted how various technologies and techniques, including Confidential Computing, can be used to go beyond just securing AI use to allowing auditing and verification of AI at various points in the process. As the CCC’s work with regulators continues, we can expect to see interest in applying CC in a broadening set of situations and sectors.

From the Outreach Committee Chair

The CCC Outreach Committee continues preparations for Confidential Computing Summit 2026, taking place June 23-24 in San Francisco, California. The event will bring together industry leaders, technology experts, and the confidential computing community to discuss the latest developments in trusted execution environments, AI security, data protection, and confidential computing adoption.

This year’s theme, “Confidential Computing is the security layer that makes agentic AI deployable at enterprise scale” will include pre-event engagement via blogs, along with LinkedIn and X posts highlighting our upcoming webinar, “Agentic AI in the Wild: Rethinking Trust when your AI has the Keys” featuring experts from Edgeless Systems, Intel, and NVIDIA. Special thanks to Rachel Wan, our Vice Chair of Outreach for moderating this. Additional highlights and social engagement will cover our keynote and speakers, each of the panels we’re participating in, and CCC sessions. Stay tuned next month for exciting updates on how we increased engagement and drove thought leadership in June.

On a related note around increasing engagement from our target audience- we’re looking forward to seeing the next iteration of the CCC website landing page. The updated design incorporates member feedback and aims to improve visitor engagement, content discoverability, and the overall user experience. Members are invited to review the proposed changes and provide feedback.

April digital marketing performance showed strong momentum, with over 9,400 page views and 4,500 visitors to the CCC website. Social media impressions increased by 64%, while engagement grew by 56% compared to previous periods.

Outreach Resources

From the TAC

May was a productive forward-looking month for the TAC, with progress across both project oversight and technical guidance for enterprise adoption of confidential computing.

A great achievement was the completion and approval to publish the TAC’s “Three Degrees” paper. The document gives adopters a practical way to think about progressive levels of confidential computing integration: from enabling confidential infrastructure, to integrating attestation with enterprise systems, to using workload-specific identity and policy. During the final review, the TAC tightened the language to make clear that the third degree is a baseline for stronger adoption rather than the end of the journey. The group also clarified that confidential computing does not remove the need to reason carefully about the software inside the trust boundary: vulnerabilities in the workload, guest kernel, firmware, or other measured components remain part of the adopter’s security model.

The TAC also received the annual update for Coconut SVSM. The project has broadened its mission from providing secure services only to confidential virtual machines to supporting confidential workloads more generally. Coconut reported continued technical progress, including APIC and VSOCK support, KBS-based attestation support, kernel-thread infrastructure, boot-flow improvements, and better CI and security practices. The project also began monthly development releases in 2025 and reported increased contributor activity across a broad set of companies and research participants. Looking ahead, the project is focused on upstream KVM/QEMU “planes” support, persistence for services such as vTPM and UEFI variable storage, CocoonFS for encrypted and integrity-protected storage, and longer-term parvisor and lightweight-workload scenarios. The discussion also highlighted potential collaboration between Coconut and Gramine around running workloads with a smaller trusted computing base.

The TAC continued work on its enterprise adoption blueprints. The clean-room blueprint was reviewed as being close to final approval, with discussion around how to explain trust in both the clean-room business logic and the clean-room infrastructure itself. The TAC also reviewed early work on the attestation and key-release blueprint, including how to present attestation policy, replay-risk mitigations, enterprise integration points, implementation guidance, and mappings to common security and compliance controls. Members noted that some of this control-mapping work may be useful beyond a single blueprint and could become reusable guidance across CCC technical documents.

The TAC also began planning updates to existing CCC technical publications. The original TAC technical white paper is being refreshed ahead of the Confidential Computing Summit so that it better reflects the current state of confidential computing, including attestation and newer deployment patterns. The terminology paper was also identified for a broader update, particularly around confidential devices, GPUs, SmartNICs, composite TEEs, containerization, and evolving workload models.

Finally, the TAC held a technical discussion on threat modeling for confidential computing in public clouds. The discussion examined how the trust model has evolved from early SGX-style enclave deployments, where the cloud service provider could often be kept largely outside the attestation flow, to modern confidential VMs and accelerator-backed systems where CPUs, GPUs, platform firmware, cloud-provided components, and high-performance devices may all contribute evidence, endorsements, and reference values. This discussion reinforced the need for CCC guidance that clearly explains what confidential computing protects, what remains in scope for platform and workload owners, and how adopters should reason about trust boundaries in real cloud deployments.

As always, TAC meeting minutes, materials, and links to recordings are available in the CCC governance repository.

Recent News

  • Landmark GDPR Guidance on TEEs from Sweden’s IMY
    • Sweden’s Data Protection Authority (IMY) has issued first-of-its-kind guidance regarding Trusted Execution Environments (TEEs) for processing personal data off-premises. Developed alongside Volvo Group, Ericsson, and CanaryBit, this report marks the first European regulatory assessment of TEEs grounded in a real operational deployment scenario, providing much-needed regulatory clarity for cloud architecture. 👉 Read the IMY Guidance Blog Post
  • New White Paper: “3 Degrees of Confidential Computing”
    • As confidential computing shifts from a niche security feature to a strategic imperative, its benefits depend entirely on stack integration depth. Led by Dan Middleton (NVIDIA / CCC Technical Advisory Council Chair), this new white paper defines a practical, 3-level maturity model to transition organizations from basic hardware isolation to full zero-trust workloads. 👉 Read the 3 Degrees White Paper (PDF)
  • Securing the Agentic AI Economy
    • Traditional security frameworks assume human-driven data movement, but autonomous AI agents operate entirely differently. A new article highlights the widening gap in enterprise security as AI agents scale in production, stressing the need for verifiable trust layers. 👉 Read the AI Agent Security Article
  • 2026 Academic Research Grant Program Open
    • The CCC is officially accepting research proposals from university faculty. This year, up to two awards will be granted for practical research focused on scalability challenges, privacy applications (data sovereignty), and architecture hardening.
    • Deadline: Applications close June 1, 2026. Recipients announced July 1.
    • 👉 Submit a Proposal / View Guidelines

In the Headline

Sweden’s Data Protection Authority Issues Landmark GDPR Guidance on Trusted Execution Environments

By Blog

Sweden’s Integritetsskyddsmyndigheten (IMY), the national data protection authority, has published a final report providing detailed legal guidance on the use of Trusted Execution Environments (TEEs) for processing personal data outside an organization’s own infrastructure. The report, released through IMY’s innovation sandbox programme, is the first European regulatory assessment of TEEs grounded in a real operational deployment scenario, conducted in collaboration with Volvo Group, Ericsson, and CanaryBit. It represents a significant step forward for Confidential Computing adoption across regulated industries.

The Use Case: Vehicle Telemetry and the Data Sovereignty Problem

The project centered on a concrete challenge in the connected vehicle space. Trucks equipped with cameras and sensors generate continuous streams of video, positioning, and telemetry data. Processing this data onboard is not technically feasible, but transmitting it to an external cloud environment raises an immediate GDPR question: once data leaves a controlled environment, does the data controller retain the technical control that Article 32 requires?

IMY examined whether TEEs – hardware-enforced enclaves in which code executes and data is processed in cryptographic isolation from the surrounding infrastructure – could provide a legally sufficient answer. The conclusion: yes, under specific architectural conditions.

What IMY Found

IMY’s report establishes several findings of broad relevance to the Confidential Computing community:

TEEs qualify as a technical safeguard under GDPR Article 32. Unlike contractual controls alone, properly implemented TEEs provide cryptographic rather than merely contractual assurance. The enclave’s isolation is enforced by hardware; it cannot be overridden by the infrastructure provider. IMY describes this as shifting the basis of trust from promises to verifiable proof.

The verifier (attestation function) is where GDPR accountability lives. IMY’s most significant finding concerns the role of remote attestation,  the mechanism, standardized in IETF RFC 9334, by which a relying party verifies that a TEE is genuine and operating in an approved state. When the data controller retains control of the attestation function and the encryption keys, IMY concludes the infrastructure provider cannot be considered a data controller or joint controller, and may not even meet the traditional definition of a data processor. Effectively, the provider supplies compute, and nothing more, because it has no technical pathway to the data.

Architectural choices determine legal outcomes. IMY’s analysis makes clear that the specific implementation matters: who controls attestation, who holds keys, and how frequently integrity checks occur all affect how GDPR roles and obligations are assigned. This provides actionable guidance for architects designing TEE-based systems in regulated environments.

Why This Matters for the Confidential Computing Ecosystem

Regulatory uncertainty has been one of the persistent friction points slowing Confidential Computing adoption. Organizations in healthcare, financial services, automotive, and other sectors understand the technical value of TEEs but have faced difficulty mapping that value onto compliance frameworks written before hardware-enforced confidentiality was practical at scale.

The IMY report, alongside prior assessments such as Germany’s BSI guidance, begins to fill that gap. It provides a jurisdiction-specific, use-case-grounded framework that compliance teams can reference, and it does so in terms that speak directly to how TEE architectures function in practice, drawing on established standards like RFC 9334.

For CCC projects and the broader open source Confidential Computing ecosystem, this kind of authoritative regulatory clarity is a meaningful accelerant. It reduces the cost and complexity of compliance analysis for organizations evaluating TEE-based architectures and establishes a precedent that other regulators across Europe and beyond may follow.

Read the Report

The full IMY publication, “Use of Trusted Execution Environment,” is available in English at imy.se.

This post was contributed by CanaryBit, a CCC member and participant in the IMY innovation sandbox project that produced the guidance described above.

AI Disclosure

This post used artificial intelligence tools for research, structural assistance, or grammatical refinement. The final content was reviewed, edited, and validated by human contributors to CCC to ensure accuracy and alignment with our community standards. We remain committed to transparency in the use of generative technologies within the open source ecosystem.

Your AI Agents Are Already in Production. Your Security Architecture Isn’t Ready.

By Blog

There’s a gap opening up in enterprise security right now, and most organizations can feel it but haven’t named it yet.

AI agents are no longer a roadmap item. They’re running in production environments, calling APIs, querying databases, reading documents, and making decisions on behalf of employees and customers. The speed of this shift has been remarkable. The security thinking hasn’t kept up.

That gap is what Confidential Computing (CC) Summit 2026 is about.

The problem with “Secure AI”

When organizations talk about securing AI, they usually mean one of a few things: access controls on who can use the model, guardrails on what the model can say, or governance frameworks for AI outputs. These are all necessary. None of them address what happens inside the computation itself.

Traditional security was designed for a world where data moved between defined endpoints, rested in known storage, and was accessed by authenticated humans. AI agents break every one of those assumptions. A single agent can autonomously traverse dozens of systems in a single session, combine sensitive data sets that were never meant to touch, and pass outputs to other agents in a chain that no human directly oversees.

The threat surface has changed. The security stack largely hasn’t.

According to IDC’s 2025 Confidential Computing Study of 600 global IT leaders, 87% of organizations identified data breaches by remote outside attackers as an area needing improvement, and 83% flagged malicious insider threats. Those numbers reflect a security posture still oriented around perimeter defense and identity management — exactly the tools that offer the least protection once an AI agent is operating inside your environment with legitimate credentials.

What Confidential Computing actually solves

Confidential Computing is the protection of data that is actively in use — during computation, not just at rest or in transit. It does this through hardware-based trusted execution environments (TEEs): isolated enclaves where sensitive workloads run encrypted and verifiably protected, even from the operating system, the hypervisor, and cloud infrastructure administrators.

This matters for agentic AI in a specific and concrete way.

When an AI agent processes your customer data, it isn’t just reading a file and returning a result. It’s loading data into memory, running inference or retrieval operations, passing context between components, and often logging intermediate states. Each of those moments is a potential exposure point. TEEs close that window. The computation happens inside a hardware-isolated environment that can cryptographically prove its own integrity to any party that asks — a capability called attestation.

Attestation is what makes Confidential Computing different from every other privacy-enhancing technology. It doesn’t just claim security. It proves it.

That distinction matters increasingly as AI systems grow more autonomous. An agent that can attest its own execution environment gives organizations something they don’t have today: a verifiable chain of trust from silicon to output.

The adoption signal is already there

IDC’s July 2025 study surveyed 600 IT leaders across 15 industries and found that 75% of organizations are already using or piloting Confidential Computing — 18% in full production and 57% actively testing. Another 19% plan to deploy within 24 months.

That trajectory is being accelerated by two forces happening simultaneously.

The first is regulatory. The EU Digital Operational Resilience Act (DORA) mandates that financial institutions maintain high standards of availability, authenticity, integrity, and confidentiality for data whether at rest, in use, or in transit. “In use” is the new requirement — and Confidential Computing is one of the few technologies positioned to satisfy it. IDC found that 77% of organizations are more likely to consider Confidential Computing specifically because of DORA’s requirements.

The second is the agentic AI wave itself. Agentic AI doesn’t just process sensitive data — it reasons across it, combines it, and acts on it in ways that amplify both the value and the risk. Organizations that want to deploy AI agents in regulated environments — healthcare, financial services, government — need a security architecture that can operate at that level of autonomy. Confidential Computing is the layer that makes that possible.

The two forces compound. Regulation creates urgency. AI creates the use case. Confidential Computing provides the infrastructure.

Where most organizations are still stuck

Despite the adoption momentum, IDC’s research surfaces a telling pattern: the barriers to Confidential Computing are no longer about whether it works. They’re about how to implement it.

The top challenge cited by 85% of respondents was validating attestation chains of trust. Seventy-eight percent flagged that it still carries a reputation as a niche technology with limited proof points. Seventy-five percent pointed to skills gaps.

These are solvable problems. But they’re not solved by waiting for the technology to simplify on its own. They’re solved through community — through practitioners sharing what they’ve built, security architects exchanging what they’ve learned, and vendors demonstrating real deployments against real threat models.

That’s precisely what CC Summit 2026 is designed to produce.

The question that matters now

75% of organizations are piloting or deploying Confidential Computing. The regulatory window is narrowing. Agentic AI is already running in production environments across every major industry.

The organizations moving fastest are the ones who stopped asking whether they need this security layer and started asking how to build it.

If you’re responsible for AI infrastructure, security architecture, or data governance in a regulated or high-stakes environment, that’s the conversation happening at CC Summit 2026.

Don’t let your security architecture fall behind your AI capabilities. The blueprints for the future of data security are being drawn right now—and you need to be in the room.

  • Secure Your Spot: Register today for the Confidential Computing Summit 2026 to connect with enterprise peers, explore real-world deployment frameworks, and solve the attestation and skills gaps holding your organization back.
  • Get Involved: Shape the standard for secure, autonomous AI. Learn how you can contribute to open-source initiatives, collaborate with industry leaders, and join the mission by becoming a part of the Confidential Computing Consortium.

Welcome to the April 2026 Newsletter

By Newsletter

TL;DR — What’s in This Issue

  • Google Cloud announced new Confidential VM support (G4 & C4) featuring NVIDIA Blackwell GPUs and Intel 6th Gen Xeon processors to secure AI workloads.
  • A modernized CCC website and customer experience project is underway, targeting a June rollout.
  • Gramine and Enarx completed annual reviews, with Gramine expanding its scope to Intel TDX VM isolation.
    • The Trustworthy Workload Identity (TWI) SIG is advancing IETF standards to help apps adopt CC without rewriting identity layers.
  • New case studies were released from TikTok (ManaTEE data clean rooms), Bosch (Hermetik data sharing), and Symphony (secure financial collaboration).
  • The 2026 Academic Research Grant program opens May 1st, and registration is open for the Open Source Summit NA and Confidential Computing Summit.

From the Executive Director 

Hello Community Member,

After a very successful OC3 last month (see our March newsletter for details), the big news is that the CCC will be a Diamond Sponsor for this year’s Confidential Computing Summit at the Mint in San Francisco on 23-24 September, hosted by Opaque and the Linux Foundation. The Call for Proposals has already closed and the schedule should be announced shortly – so please head over to check it out.

As well as conferences devoted to Confidential Computing, I’m pleased to see increasing interest in Confidential Computing at industry events around the world.  As well as CC appearing as a topic at blockchain and Web3 conferences (addressing use cases that appear to be gaining significant traction in those sectors), we’re seeing it turning up in other interesting places, as well: Open Source India (Mumbai, 16-17 June) has four separate sessions on different aspects of Confidential Computing.

We’re always looking to highlight Confidential Computing across the world, so if you’re aware of sessions, conferences, webinars or workshops where CC is featured, please get in touch!  Equally, if you’re organising any sort of gathering or meet-up where the attendees might be interested in learning more about any aspect of Confidential Computing and how it can be used, please let us know: we love finding ways to spread the word!

From the Outreach Committee Chair

April bloomed bright with opportunities to reimagine the Confidential Computing Consortium  website and overall customer experience. A new and modernized customer experience has been drafted and introduced to the consortium.There is a lot of excitement around this from multiple partners across the consortium. The goal is to see a complete redesign that can be rolled out in June.If you would like to provide insights, we welcome them! Contact either Rachel or myself to join this workstream.

The CCC Outreach session in OC3, Creating Global Standards for Confidential Computing, is now live on Youtube. Member companies from the Confidential Computing Consortium shared how they and their customers use Confidential Computing to enable their business:

  • Symphony leverages Google Cloud Confidential Space to provide secure, cloud-native data processing and collaboration for financial institutions, ensuring that sensitive data remains isolated from the cloud provider and system administrators.
  • Google is transforming digital advertising with Confidential Matching, utilizing TEEs to allow advertisers and platforms to match data and perform retargeting without either party ever gaining access to raw personally identifiable information (PII).
  • Bosch introduced Hermetik, a trustworthy collaboration service built on Intel TDX that enables secure, multi-party data sharing and shared governance across the automotive, healthcare, and manufacturing sectors.
  • Huawei showcased their Kunpeng AI solution, which extends Trusted Execution Environments to hardware accelerators like GPUs and NPUs, allowing for high-performance AI processing while maintaining full data protection.
  • Super Swarm by Super Protocol is pioneering a standard protocol called “HTTPS for AI” that provides verifiable privacy for clinical AI and has demonstrated the ability to reduce complex compliance audit times from four weeks down to just two hours.
  • TikTok shared their ManaTEE approach, an open-source two-stage data clean room that enables developers to build AI models using synthetic data before executing them against sensitive real-world data within a secure TEE.

Outreach Resources

From the TAC

We had a productive April in the TAC. We’ve made progress on our enterprise integration blueprints and should have some of them published next month. We also featured annual reviews from two of the CCC’s longest-running projects, Enarx and Gramine. We also had a tech talk from one of our newest SIGs on trustworthy workload identity for replicated workloads.

Enarx remains the CCC’s only TEE-agnostic, WebAssembly-based runtime — a single workload binary that runs unmodified across SGX, SEV-SNP, and other TEEs. Richard Zak continues to maintain the project, and the TAC heard that companies are still actively reaching out about the TEE-agnostic, WASM-based isolation model Enarx pioneered. Anyone evaluating cross-TEE portability or looking to contribute should engage with the project — the architecture is differentiated and the door is open for new collaborators.

Kailun Qin and Mona Vij presented the Gramine annual review, with Don Porter. Gramine continues to see broad production adoption as the leading LibOS for lift-and-shift Linux workloads in TEEs. The project recently won the ACSAC Cybersecurity Artifact Award and has expanded scope from SGX process isolation to TDX VM isolation, reusing a substantial portion of its hardened LibOS to offer a tighter security footprint than general-purpose Confidential VMs (see the Gramine-TDX paper at ACM CCS). With a healthy user base and a clear technical roadmap, Gramine is well positioned for new contributors and sponsoring members to step in alongside the existing maintainers.

Tech Talk: Trustworthy Workload Identity for Replicated Workloads (April 16). Mark Novak (JPMorgan Chase), chair of the CCC Trustworthy Workload Identity (TWI) SIG, presented the SIG’s work on extending workload identity to replicated workloads — binding identities to attested workload instances using RATS-based remote attestation. The work feeds the IETF WIMSE draft (draft-ccc-wimse-twi-extensions) co-authored across JPMC, Arm, and Fraunhofer SIT, and is aimed at letting existing applications adopt Confidential Computing without rewriting their identity layer.

You can always find historical minutes, materials, and links to recordings in our governance repo.

Recent News

  • At 2026 Google Cloud Next conference, Google has announced Confidential Computing support for G4 VMs in partnership with NVIDIA, featuring NVIDIA RTX PRO 6000 Blackwell Server Edition GPUs on Google Compute Engine (GCE) Confidential G4 VMs, available in preview globally, to help strengthen confidentiality and integrity for a wide spectrum of sensitive AI workloads. In partnership with Intel, Google is introducing the preview of C4 Confidential VMs, bringing Intel TDX to 6th Gen Xeon processors to help protect diverse AI and analytics workloads while providing industry-leading compute density and performance. Read more: https://blogs.nvidia.com/blog/google-cloud-agentic-physical-ai-factories/
  • CCC members Invary, Anjuna Security, and Phala will present at Confidential AI Systems on May 6, a free virtual event exploring how enclaves, attestation, and AI agents work together to protect sensitive data. Register here.
  • The CFP is now open for the CCC Academic Research Grant Program 2026. Up to two awards will support practical research advancing confidential computing, with focus areas including scalability challenges, privacy-focused applications, and security hardening and verification.May 1: Applications open | June 1: Applications close | July 1: Recipients announced. Learn more. 
  • CCC will be at Open Source Summit North America. Join Mike Bursell and Christopher Robinson (OpenSSF) for a session on the “taxonomy of personae” impacting security. Save $699! Use code SPRING when you register.May 19 | 2:10pm | Session details | Register now.

Secure AI will be a key focus at the Confidential Computing Summit, taking place June 23–24 in San Francisco. CCC is a Diamond Sponsor for this year’s event, which brings together global leaders working on privacy-preserving, production-ready AI.
Learn more and register.

Securing the Agentic Future: The CCC Responds to AI Security Consultations on Both Sides of the Atlantic

By Blog

The Confidential Computing Consortium (CCC) has recently submitted formal responses to two major government consultations on AI security: the US National Institute of Standards and Technology (NIST) Request for Information on the secure development and deployment of AI agent systems (NIST-2025-0035), and the UK Government’s Department for Science, Innovation and Technology (DSIT) Call for Information on Secure AI Infrastructure. Taken together, these responses make a consistent and compelling case: as AI systems become foundational to national security, public services, and economic competitiveness, hardware-enforced trust must become a foundational layer of AI infrastructure.

A Shared Threat Landscape

Both responses begin from the same premise: AI agent systems face a category of risk that conventional cybersecurity tools were not designed to address. The threats are not merely traditional data breaches, they target the unique characteristics of AI itself.

Key risks highlighted across both submissions include:

  • Model weight theft, where proprietary model weights can be exfiltrated through API abuse or direct memory dumps by malicious insiders or compromised infrastructure
  • The infrastructure trust gap, where standard cloud security protects against external attackers but leaves model weights and inference data accessible to the cloud provider’s hypervisor or privileged administrators
  • Memory scraping and cold boot attacks, which can extract sensitive context, credentials, or cryptographic material from unprotected RAM
  • Memory poisoning, where adversarial content injected into an agent’s long-term memory is triggered later, with the temporal gap between injection and execution making detection very difficult
  • MCP-specific threats (highlighted in the NIST response), including shadow servers, tool poisoning, and confusion attacks that undermine the integrity of agent-to-tool communication
  • “Confused deputy” attacks in multi-agent systems, where a compromised agent manipulates another into sharing sensitive data without adequate authentication

Why Confidential Computing Is the Answer

The central recommendation of both responses is that protecting AI systems requires moving beyond perimeter-based controls toward architectures rooted in hardware-enforced trust; specifically, attested, hardware-based Trusted Execution Environments (TEEs).

Confidential Computing addresses several of these risks directly:

  • Data-in-use protection encrypts agent memory and model weights during processing, ensuring that even cloud providers and privileged infrastructure operators cannot access sensitive workloads
  • Remote attestation cryptographically verifies that the correct, unmodified agent code is running on a genuine, trusted platform before any secrets are released, providing technical guarantees rather than mere contractual assurances
  • Cryptographically assured workload identity gives each agent an ephemeral identity rooted in hardware attestation, replacing static API keys with dynamic, verifiable credentials
  • Key Broker Services release decryption keys and credentials only after successful attestation, meaning that if the environment doesn’t match an approved policy, keys are simply not released
  • Confidential Inference (highlighted in the UK response) keeps user prompts encrypted in transit, decrypting them only inside an attested TEE, preventing cloud operators or intermediaries from accessing prompt contents

The UK response also draws attention to the need to extend these protections to accelerators such as GPUs, which in multi-tenant environments represent a significant attack vector, and to future-proof the transport layer against “Store Now, Decrypt Later” attacks using Post-Quantum Cryptography (PQC).

Looking Ahead: Agentic Zero Trust and Standardisation

As AI agents become more capable and autonomous, potentially holding wallet keys, signing transactions, and communicating with other agents, the CCC’s responses call for a shift toward what we describe as Agentic Zero Trust: a model where every inter-agent interaction is cryptographically authenticated, and where an agent’s identity is bound to its code measurement rather than a pre-shared secret.

Both responses also call on governments to take an active role in standardisation. The NIST response urges the US to define clear “Confidential AI” assurance levels so that AI providers can credibly demonstrate they are technically unable to access user data. The UK response similarly highlights the need to standardise attestation reports across hardware vendors – AMD, Intel, Arm, and NVIDIA – to enable a unified root of trust across the UK AI sector.

On the supply chain side, the NIST response raises a specific concern: MCP authentication is currently optional by design and package signing is inconsistently required, creating risks at every startup. Both responses make clear that governance assurances are not a substitute for cryptographic guarantees.

Read the Full Responses

These are just highlights from two detailed submissions that together cover threat modelling, technical controls, patching challenges for stateful agents in TEEs, monitoring constraints imposed by Confidential Computing, and much more.

Read the CCC’s full response to NIST-2025-0035 →

Read the CCC’s full response to the UK Government’s Secure AI Infrastructure Call for Information →

Welcome to the March 2026 Newsletter

By Newsletter
March2026

TL;DR — What’s in This Issue

  • Confidential Computing gained strong visibility this month through OC3, GTC, and KubeCon EU, reflecting a maturing ecosystem with more open discussion of technical, regulatory, and strategic challenges.
  • The TAC advanced key policy and technical work, including responses to NIST and UK government consultations and progress on guidance documents to help organizations adopt Confidential Computing more effectively.
  • Looking ahead, engagement opportunities continue to grow, including CCC resources for members and the upcoming CC Summit 2026, with session and panel proposals due April 8.

From the Executive Director 

Hello Community Member,

One of the big Confidential Computing conferences of the year happened this month: OC3 in Berlin (and virtual).  The CCC was a sponsor and had two sessions in a packed program – one on regulations and standards (which I presented in person) and one introducing the work of the consortium (which was presented remotely by Rachel Wang, vice chair of the Outreach Committee).  There were, however, multiple sessions by CCC members, including, of course, Edgeless Systems, who run the event.  A number of people have commented on how the industry and ecosystem seem to be maturing, but also on the honesty of many of the sessions.  This might seem to be an odd word to use, but as an industry becomes more established and sure of itself and its future, it makes sense that we can discuss challenges that we face – regulatory, technical, tactical and strategic – in the knowledge that these are not existential threats, but issues that can be openly explored and don’t need to be hidden.

One of the most important parts of the CCC’s mission is allowing organizations and experts from across the industry and ecosystem to work together to resolve these sorts of challenges.  As a part of the Linux Foundation, and with our anti-trust policy firmly in place since our foundation, our committees and special interest groups (SIGs) offer a safe place to discuss and work on tricky issues.  We also strive to provide a safe and welcoming set of spaces for all types of discussion.  While members may not always agree with each other (it would probably be more worrying if they did!), we attempt to navigate the various viewpoints that come up and, where we need to express an opinion or publish materials, to work towards a consensus.  Please join one of our meetings to find out more – or catch up with previous meetings by watching them on our YouTube channel.

Outreach

As Mike mentioned above, this month marked an exciting time for Confidential Computing awareness! 

OC3 brought together the Confidential Computing community in Berlin for 27 talks spanning hardware, cloud platforms, attestation, and AI. Our event recap highlights key themes, insights, and takeaways from the conversations shaping the future of confidential computing. Read the recap.

At GTC, the CEO of NVIDIA highlighted the “incredible importance” of Confidential Computing in his keynote and shared how security across the whole stack was required to drive AI and data sovereignty advancements. Intel and others also showcased real world examples of Confidential Computing on the show floor and across multiple co-hosted sessions that featured thought leaders from Google, NVIDIA, Opaque and the Technology Innovation Institute (TII). The GTC Shift that Put Confidential AI at the Center of Everything podcast by Opaque highlighted the news around CC and how it is securely advancing AI around the world.

At KubeCon EU, we saw a new announcement from Red Hat and NVIDIA around the Cloud Native Computing Foundation’s (CNCF) Confidential Containers community, in addition to a tech preview for the GPU on OpenShift.

And a reminder that CC Summit 2026, which is coming June 23-24 to SF, has opened their Call for Proposals HERE. The deadline is April 8th to get the Session Presentation (25 Minutes Including Q&A) and Panel Discussion (25 Minutes Including Q&A) proposals submitted. Notifications of acceptance will be shared on May 4th.

Outreach Resources: 

From the TAC

The TAC has had a productive March focusing on industry-level guidance and regulatory engagement. We successfully finalized and submitted our response to the NIST RFI regarding AI safety and security standards. Furthermore, we concluded our response to the UK Government’s Call for Evidence on AI and data privacy, emphasizing the critical role of Confidential Computing in securing sensitive workloads across international borders. These efforts ensure the Consortium’s technical perspective is represented in the frameworks that will govern the next generation of computing infrastructure.

Internal workstreams have made substantial progress on our suite of technical guidance documents. We are nearing completion on two of the three documents we outlined last month. This month also saw the launch of a fourth technical document focused on integration levels. This new workstream aims to clarify the role of integration in realizing the benefits of Confidential Computing – helping organizations navigate the technical trade-offs between security depth and operational ease.

These documents directly address the implementation challenges identified in recent market research, particularly the need for standardized paths to bridge the industry-wide skills gap. As the market moves beyond early pilots, providing these clear, architecturally agnostic roadmaps is the TAC’s primary focus. We invite all technical representatives from our member companies (and unaffiliated experts) to join these weekly sessions to ensure our guidance reflects the full breadth of the current landscape.

Recent News

  • OC3 Recap
    • At OC3 2026, the global Confidential Computing community gathered in Berlin and online to discuss how the ecosystem is advancing secure computing for AI, cloud infrastructure, and protecting sensitive data in use. Our event recap highlights key themes, insights, and takeaways from the conversations shaping the future of confidential computing. Read the recap.

Let’s grow our community!  Share this with your network.
Subscribe to CCC Newsletter